
Compliance that clears the review, and holds up after it.
Regulated businesses carry overlapping obligations, ADA and WCAG accessibility, CIPA and GDPR consent, HIPAA health-data rules. Agency 39A audits, remediates, and monitors across all of them, so your site passes security and compliance review and stays defensible, engineered in, not bolted on after a demand letter arrives.
Request a compliance audit
Coverage across the regulations that put your site at risk
Section 508, ADA & WCAG 2.2 AA
The accessibility standard U.S. courts and the DOJ's 2024 web rule measure against. We audit the full WCAG 2.1/2.2 AA success criteria and remediate what fails, in code and design, never an overlay widget.
Explore →CCPA, CPRA, CIPA & GDPR consent
California's wiretapping law (CIPA §631/§632.7) and the EU's GDPR/ePrivacy rules both turn on consent for trackers, chat, session replay, pixels, cookies. We inventory what fires, implement consent-first tracking, and cut the exposure while keeping analytics and ads running.
Explore →HIPAA Compliance
Handling PHI in websites, forms, or marketing pulls you into HIPAA. We map the data flows, remove unsafe tracking, and put the safeguards and BAAs in place.
Explore →Coverage across the regulations that put your site at risk
Your Compliance Gap Is an Existential Threat: CIPA, CCPA, GDPR, and HIPAA in 2026
Digital privacy compliance is an arcane subject that sits in the grey space between general counsel, IT, and marketing, each business unit with an opinion, almost none with an answer. Privacy compliance is a whole-digital business operations problem, and when the complaint arrives, which it will, you need to understand where your policies, technologies, and organizational behaviors stand.
Five ways we keep regulated sites compliant
Compliance audit
A full audit across accessibility, consent and tracking, and data handling, automated scanning plus hands-on manual review, mapped to the specific rules that apply to you, not a raw tool dump.
Code & design remediation
We fix what the audit finds in the codebase and design system, accessibility, tracker and consent behavior, and data flows. Real fixes your team can ship, never an overlay.
Consent & tracking implementation
Consent-first tracking, Consent Mode and Usercentrics, that keeps analytics, ads, and attribution running while meeting CIPA, GDPR, and CCPA obligations.
Documentation & attestations
VPATs, accessibility statements, DPAs and BAAs, and the conformance records your legal and procurement teams need on file.
Monitoring & regression prevention
Compliance checks wired into your build and scheduled re-testing, so new pages and releases stay compliant instead of drifting back out.
Not sure where your compliance gaps are?
We run the same checks a plaintiff's firm or auditor would, accessibility, tracking and consent, data handling, then come back with the gaps that create real exposure and which ones matter most.
Request a compliance exposure checkHow we work
Audit against real standards
We test against the WCAG criteria, consent rules, and data-handling standards regulators and plaintiffs' firms actually cite, automated plus manual, so nothing hides behind a green score.
Remediate and implement controls
We fix findings in the codebase and design system and put the consent and data-handling controls in place, durable fixes, not a widget painted over the problem.
Monitor and prevent regression
We wire compliance checks into your build and re-test on a schedule, so new releases stay compliant instead of quietly drifting out.
agency 39A CASE STUDY

Agency 39A led CLSI’s end-to-end digital transformation — one strategy uniting a rebuilt Umbraco CMS, HubSpot CRM and marketing automation, NetForum integration, and the new myCLSI member experience. Six months in: subscription traffic up 145%, embedded CTAs converting at 48%, and site search engagement up 70%.
View Case Study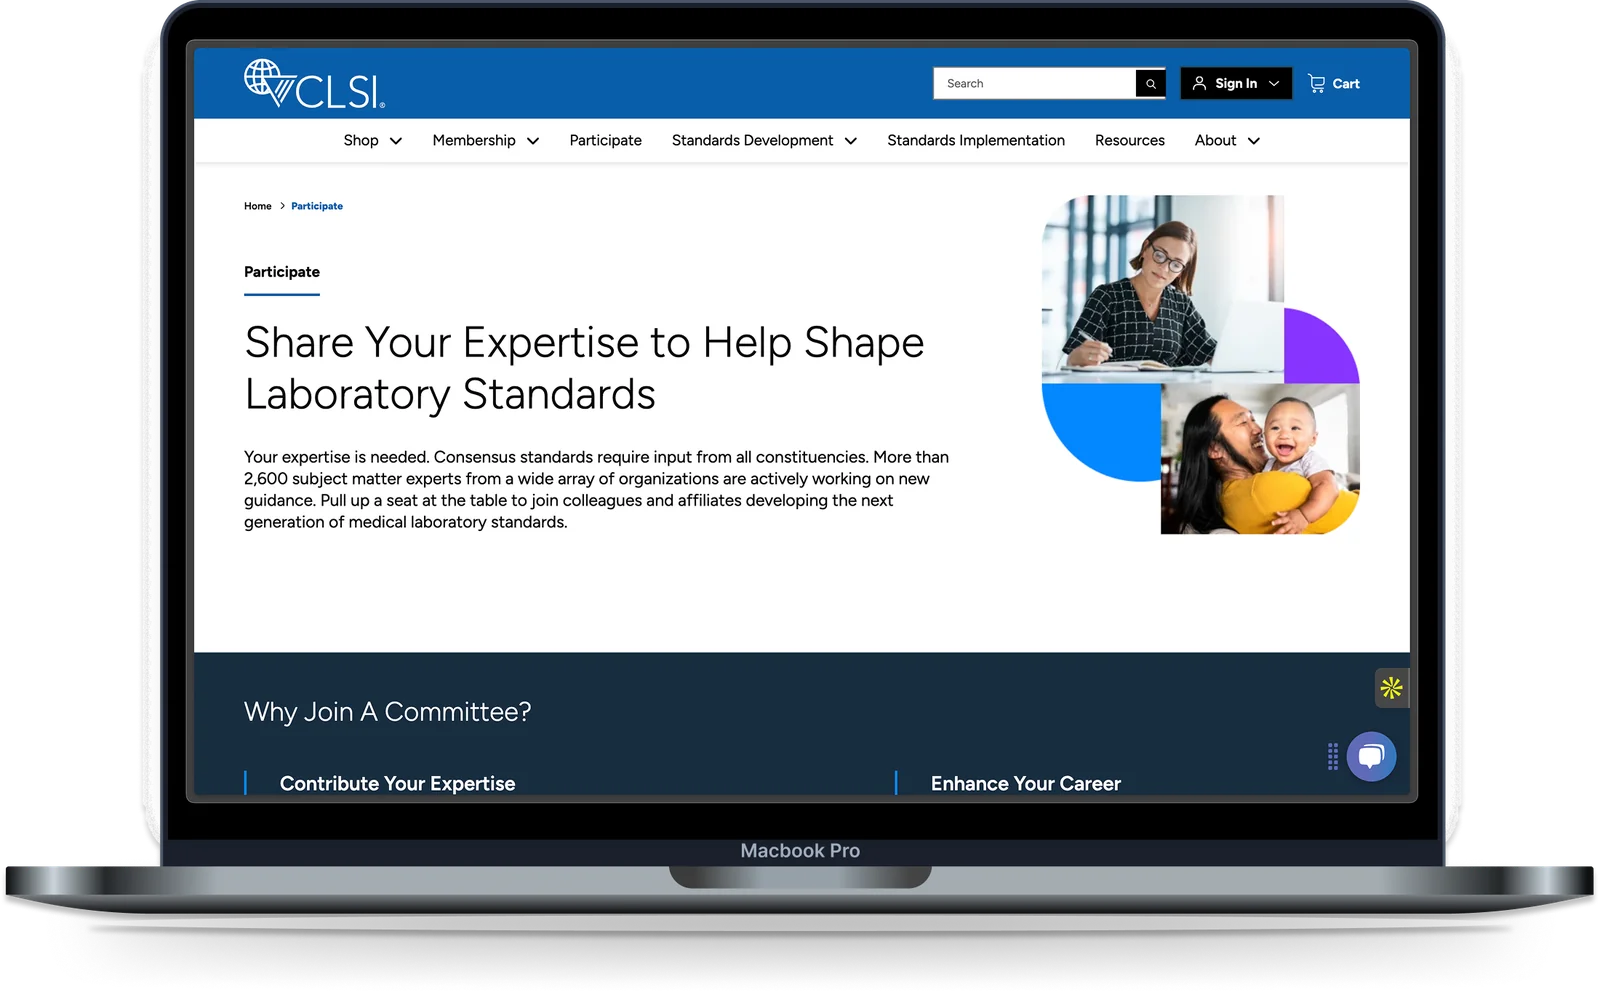
Let's talk
Meet our team, ask questions, and get the answers you need to move forward and improve your digital strategy.
What our clients say
“Agency 39A’s expertise in design and development - paired with their strong understanding of the healthcare industry - has made them a perfect fit partner for San Ysidro Health. The team is professional, responsive, knowledgeable, and kind. With their help, we’ve revolutionized our digital presence for patients and are already seeing the benefits!”
Brett
/
San Ysidro Health

What compliance does a regulated-industry website need?
How quickly can you remediate a compliance gap?
It depends on the site, but we prioritize the highest-exposure issues first, the consent and tracking leaks and the accessibility failures that carry legal weight, so the most serious risk is reduced early while the full remediation continues.
What is digital compliance?
Digital compliance is bringing your website and applications in line with the accessibility, privacy, and consent rules that govern public-facing digital experiences, including ADA and WCAG accessibility, CIPA and GDPR consent, and CCPA data rights. It reduces legal exposure while keeping the experience usable for everyone.
Is digital compliance the same as SOC 2?
No. SOC 2 protects your internal systems and the data they store, such as intellectual property, client payment details, and account information. Digital compliance, HIPAA, CIPA, CCPA, GDPR, and ADA, protects the privacy and rights of everyone who visits your website, whether they knowingly provide information or not. Its scope is much wider, because it reaches every visitor, not just your internal environment. Compliance and performance do not have to be in conflict, and the right setup meets the standard while keeping your site optimized for growth.
Which industries do you work with?
Healthcare, life sciences, and other regulated and complex B2B organizations, the businesses that carry the heaviest overlapping compliance obligations.
Do you fix the problems, or just report them?
Both. We audit, then remediate in the codebase and design system, implement the consent and data-handling controls, and put monitoring in place so you stay compliant as the site changes.
How do I know if my site is at risk?
A compliance audit shows what your site is actually doing: whether it meets WCAG, what trackers fire before consent, and whether any tools receive protected or regulated data. That tells you where the real exposure is.
What web-compliance obligations do regulated businesses have?
Most face several at once: accessibility under ADA and WCAG, consent and tracking under CIPA, GDPR, and state privacy laws, and health-data rules under HIPAA. Which apply depends on your users, your data, and where you operate.